• 135: The Cassandra Panel: OT Threat Intelligence from April to September 2026
    Oct 6 2026

    The Cassandra Panel: OT Threat Intelligence from April to Now

    Bryan Singer revisits an April threat briefing to ask what changed in six months, and the answer is a lot. Georgia Tech's Saman Zonouz shares research on thousands of internet-exposed PLCs, web-enabled controllers, shared firmware code across vendors, and exposed solar inverters. Daryl Haegley explains why threat intel has to start with knowing what's inside the fence, and Brad Willet brings the asset owner's view: stray contractor routers, insider risk, and why no newsletter replaces a trusted network. Vivek dubbed it "the Cassandra Panel" for a reason.

    Guests: Saman Zonouz (Georgia Tech); Daryl Haegley (Department of War); Brad Willet (UPS) Host / moderator: Bryan Singer

    Chapters: 00:00 April recap: nothing sophisticated about it 03:53 Georgia Tech CPSEC and anonymous incident reporting 11:35 What changed since April 13:44 Looking inside the fence 16:08 How the Iranian campaign is progressing 18:37 Internet exposure and inventory 23:27 Not fighting the last war 24:51 Capacity gaps and web-enabled PLCs 28:53 Inside-out threat intelligence 33:38 Relationships as threat intel 37:08 Contractors, modems, and insiders 41:14 SBOM and shared firmware code 43:03 Impact-first risk and wrap-up

    Recorded at the CS²AI Online Symposium, "Level Zero: Visions & Reflections."

    Join us at Level Zero 2027, April 23–30 at Georgia Tech in Atlanta: pre-conference training, the Conflag Zero™ tabletop exercise, and three days of practitioner-led sessions built so you can put what you learn to work the Monday you get back.

    Questions: info@levelzeroconference.com · Sponsorship: sponsor@levelzeroconference.com Produced by CS²AI (Control System Cyber Security Association International).

    Mehr anzeigen Weniger anzeigen
    46 Min.
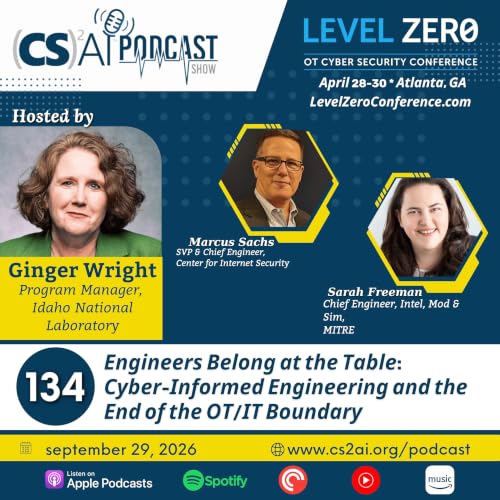
  • 134: Engineers Belong at the Table: Cyber-Informed Engineering and the End of the OT/IT Boundary
    Sep 29 2026

    Three veterans of critical infrastructure security trace how the field went from arguing that infrastructure was even a target to treating digital risk as an engineering hazard. Ginger Wright, Sarah Freeman, and Marc Sachs define cyber-informed engineering in plain terms, share real examples of consequences engineered out of a system, explain why adversaries already read your engineering documentation, and make the case that engineers don't need to become hackers to belong in this conversation. They close with why engineers should come to Level Zero.

    Guests: Sarah Freeman (MITRE); Marc Sachs (Center for Internet Security) Host / moderator: Ginger Wright (Idaho National Laboratory)

    Chapters: 00:00 Welcome and panel introductions 02:52 Why engineering is up first at Level Zero 04:24 From 'not a target' to target du jour 08:03 Y2K to WannaCry: when the OT/IT boundary became fiction 12:28 Engineering out the consequence (NIST 800-82 Rev. 3) 14:31 Why engineers belong at the table 19:01 Digital risk and defining CIE / CCE 22:13 Real examples of designed-out consequences 28:34 Where CIE runs into regulation 32:40 Engineer pushback and 'fighting the scenario' 37:01 Digital risk is just another hazard 40:01 The five whys, and why come to Level Zero

    Recorded at the CS²AI Online Symposium, "Level Zero: Visions & Reflections."

    Join us at Level Zero 2027, April 23–30 at Georgia Tech in Atlanta: pre-conference training, the Conflag Zero™ tabletop exercise, and three days of practitioner-led sessions built so you can put what you learn to work the Monday you get back.

    Questions: info@levelzeroconference.com · Sponsorship: sponsor@levelzeroconference.com Produced by CS²AI (Control System Cyber Security Association International).

    Mehr anzeigen Weniger anzeigen
    43 Min.
  • Episode 133: Engineering Expertise: Core Skills for ICS/OT Cybersecurity with Marcus Sachs, Patrick Miller and Christian Harter
    Aug 18 2026

    Solving the OT Talent Puzzle: A Career Roadmap from Three Industry Veterans

    Derek Harp sits down with Marcus Sachs (Center for Internet Security), Patrick Miller (Ampyx Cyber), and Christian Harter (UPS) for a candid conversation about breaking into — and building a career in — ICS/OT cybersecurity. The panel tackles the IT/OT divide, why "dropping your ego" matters more than any certification, how AI is reshaping the skills employers want, and why old-school, face-to-face networking still beats the resume-screening algorithms. Whether you're a plant engineer eyeing cybersecurity or a security pro trying to understand the physical world, this episode is a practical roadmap for finding your way in.

    Mehr anzeigen Weniger anzeigen
    1 Std. und 15 Min.
  • 132: Solving Problems at Scale: Kenny Mesker on OT Cybersecurity Strategy, Risk, and Leadership
    Jun 2 2026

    Kenny Mesker, OT Cybersecurity Strategist and Distinguished Engineer at Chevron, joins Derek Harp to share his remarkable journey from growing up on a farm in West Texas to becoming one of the industry's leading voices in operational technology (OT) cybersecurity.

    With more than 30 years of experience spanning electric utilities, SCADA systems, industrial control systems, and cybersecurity, Kenny reflects on the evolution of OT security from the days of air-gapped networks to today's interconnected digital environments. He discusses how a passion for problem-solving led him from electrical engineering into industrial operations and ultimately into cybersecurity strategy.

    Kenny offers practical advice for professionals looking to enter the OT cybersecurity field, explaining why hands-on operational experience remains one of the most valuable foundations for success. He also explores the challenges of IT/OT convergence, the importance of risk assessment, and how cybersecurity leaders must think beyond individual systems to protect entire organizations and critical infrastructure.

    Looking ahead, Kenny shares his perspective on artificial intelligence, cloud technologies, and the future of OT architectures, highlighting both the opportunities and challenges these emerging technologies will bring to industrial environments.

    Whether you're an engineer, cybersecurity professional, student, or industry leader, this episode provides valuable insights into building a successful OT cybersecurity career while helping protect the systems that power modern society.

    Mehr anzeigen Weniger anzeigen
    46 Min.
  • 131: OT Monitoring & SOC and Incident Response — Lessons from the Field with Cambios Academy
    Feb 4 2026

    In this episode of the (CS)²AI Podcast, host Derek Harp is joined by Jonathan Pollet, Marc Visser, and Bryan Singer for a deep-dive Q&A discussion following CS2AI’s January 21st community event on OT Monitoring & SOC and Incident Response. Drawing on decades of hands-on experience across industrial environments worldwide, the panel expands on questions that couldn’t be fully addressed during the live sessions.

    The conversation explores why OT monitoring and SOC capabilities must come before incident response, and how poor network architecture, lack of visibility, and organizational silos continue to undermine response efforts when incidents occur. Jonathan outlines the architectural foundations required to support effective detection, response, and recovery, while Marc emphasizes the practical realities of implementing OT monitoring—from working with factory engineers to reducing alert fatigue and building usable SOC workflows.

    Bryan brings the incident responder’s perspective, sharing real-world insights from global OT incidents, including prolonged dwell times, ransomware impacts on production, and why organizations without proper segmentation and monitoring often experience the most severe and prolonged outages. The discussion also tackles common questions around Fusion SOCs vs. dedicated OT SOCs, the human challenges of translating OT data into actionable intelligence, and what asset owners should realistically expect from incident response retainers.

    This episode is a must-listen for OT practitioners, security leaders, and asset owners looking to move beyond theory and understand what actually works in the field. Whether you are just beginning your OT monitoring journey or refining mature SOC and IR capabilities, this discussion offers practical guidance rooted in real operational experience.

    Mehr anzeigen Weniger anzeigen
    43 Min.
  • 130: S4’s “Connect” Theme Explained — Dale Peterson on OT Security’s Hyper-Connected Future
    Jan 14 2026

    In this episode of the (CS)²AI Podcast, host Derek Harp is joined once again by Dale Peterson, Founder of the S4 Conference and one of the longest-standing voices in OT cybersecurity. As Dale marks 25 years in the industry, the conversation takes a forward-looking turn toward what he believes is the next major inflection point for industrial security: connectivity driven by AI, data, and business systems.

    Dale explains why the 2026 S4 Conference theme, Connect, is not just about networking people, but about the explosive growth of connections between OT systems, enterprise platforms, and analytics driven by AI. From MES, ERP, and PLCs to asset inventories and security telemetry, these connections are accelerating faster than most security teams are prepared for—often driven by business value rather than security design.

    Listeners will hear why manufacturing is emerging as the epicenter of this transformation, how AI is enabling real-time querying across operational systems, and why OT security teams must prepare for a future where their tools become just another data source in larger operational workflows. Dale also shares how this shift will reshape risk, attack surfaces, and even the role of humans in control and response.

    The episode also provides an inside look at S4 2026, including this year’s Proof-of-Concept Pavilion, where vendors will be forced to demonstrate their technologies live on a real manufacturing environment, as well as updates on attendance, ticket availability, and why this will be the final year S4 is held in Miami Beach before moving back to Tampa.

    This is a must-listen for OT security professionals, automation leaders, and anyone trying to understand how AI-driven connectivity will redefine both risk and opportunity across industrial environments in the years ahead.

    Mehr anzeigen Weniger anzeigen
    31 Min.
  • 129: Why OT Cybersecurity Isn't a One-Tool Problem: Insights to be discussed at Level Zero
    Mar 27 2025

    In this insightful episode of the (CS)²AI Podcast, host Derek Harp welcomes Jay Gignac, Vice President of Sales at FoxGuard Solutions, (CS)²AI Fellow and a passionate OT cybersecurity evangelist. The conversation centers around some of the most pressing challenges in the control systems industry—asset visibility, patch management, and community collaboration. Jay, who will be speaking at the upcoming Level Zero OT Cybersecurity Conference, offers expert-level advice for professionals navigating the complex world of operational technology security.

    Listeners will hear real-world examples of how OT differs from IT, particularly in areas like patching and compliance. Jay shares how asset discovery and lifecycle management remain fundamental hurdles, even after over a decade of cybersecurity initiatives. The discussion explores the nuances across industry verticals—energy, manufacturing, oil & gas—and underscores why tailored approaches are critical when securing diverse OT environments.

    This episode is a must-listen for OT professionals, cybersecurity leaders, and anyone attending Level Zero or looking to deepen their understanding of control systems security. Discover why collaboration, not just technology, is key to long-term success in the OT space. Whether you’re an engineer, a procurement officer, or a seasoned CISO, there’s valuable insight here for everyone working to protect the core of their company’s operations.

    Mehr anzeigen Weniger anzeigen
    15 Min.
  • 128: From the Pentagon to Public Safety: Lucian Niemeyer’s Mission to Secure OT
    Feb 18 2025

    Lucian Niemeyer, Chief Executive Officer of Building Cyber Security and former Assistant Secretary of Defense, joins Derek Harp to discuss the growing cyber risks to operational technology (OT) systems and the urgent need for proactive frameworks to protect public safety. Recorded live at Hack the Capitol 7.0, this episode delves into the vulnerabilities in smart buildings, connected infrastructure, and critical systems that could have life-threatening consequences if exploited.

    Lucian shares how his experience in national security shaped his focus on OT cybersecurity, emphasizing the physical impacts of cyberattacks on HVAC systems, elevators, and even water utilities. He introduces the concept of cyber commissioning, a process that ensures building systems are configured securely from the start. Lucian also explains how Building Cyber Security is creating industry-specific frameworks to help facility managers, building owners, and policymakers mitigate risks and reduce insurance liabilities.

    With increasing threats from ransomware, nation-states, and insider errors, this episode highlights why securing operational technology is critical to protecting both property and lives. Learn how Lucian’s nonprofit is driving collaboration across industries to address this rapidly evolving threat landscape.

    Mehr anzeigen Weniger anzeigen
    28 Min.